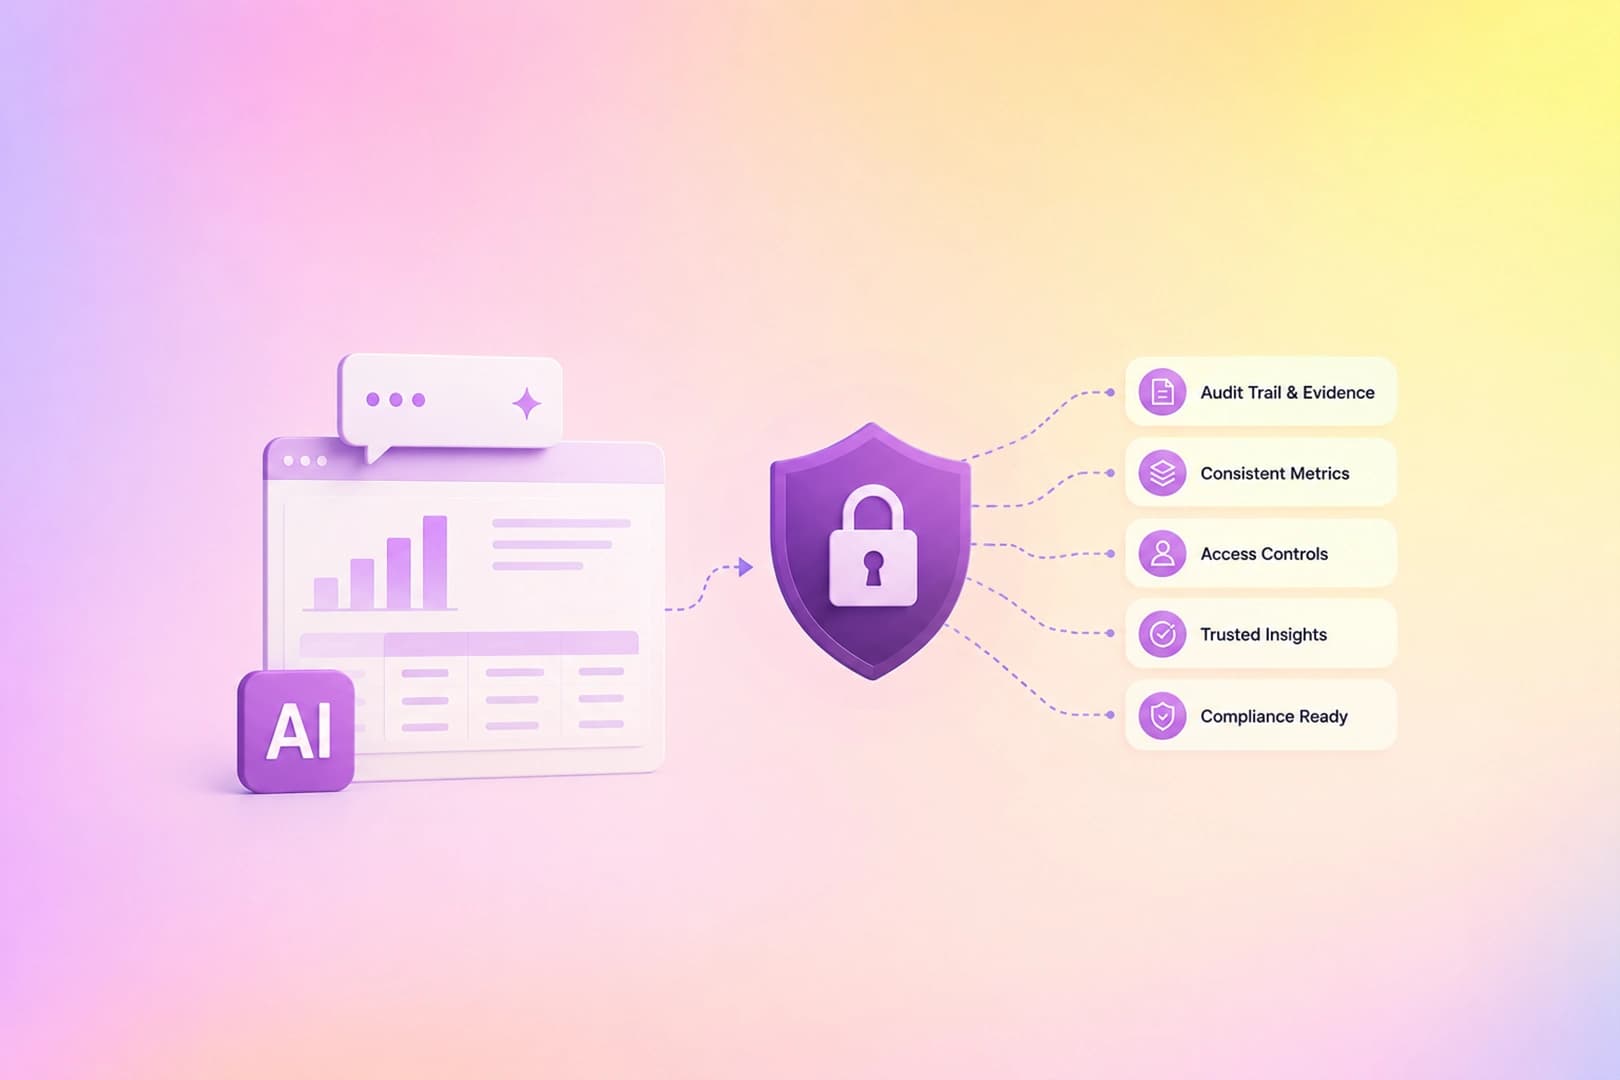
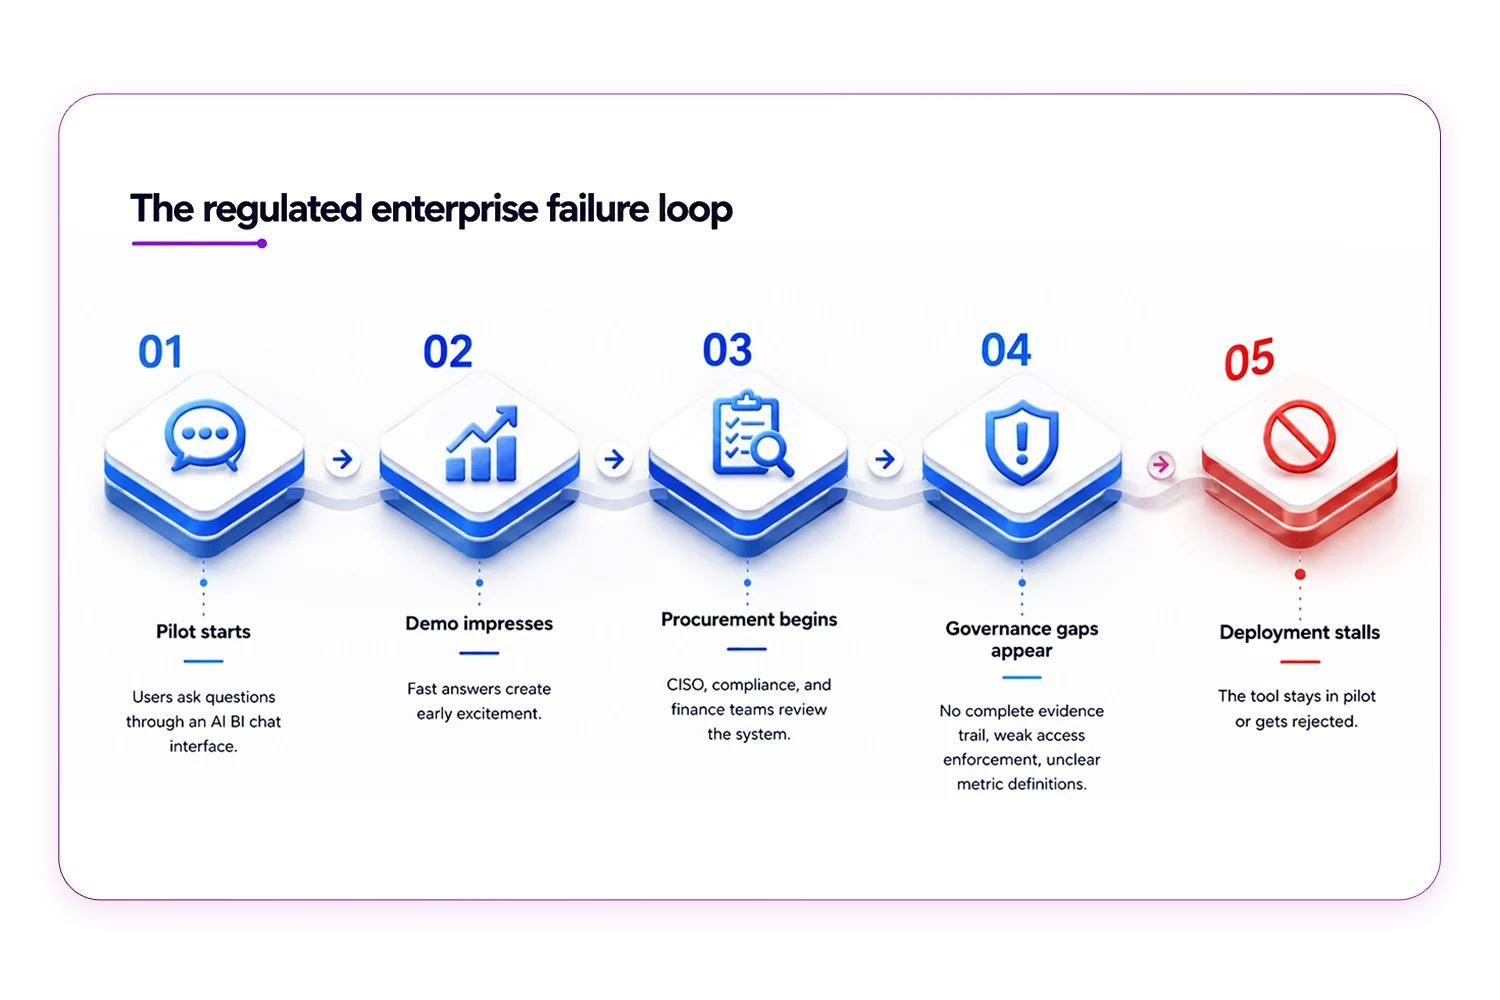
Regulated enterprises do not get to fail quietly. When a bank, an insurer, or a health system deploys analytics software that produces an indefensible number, the consequence is not an internal retrospective. It is an audit finding, a regulatory inquiry, or a remediation programme with a budget line. This is why the wave of “AI BI” tools, chat interfaces bolted onto warehouses with a capable model underneath, keeps stalling at exactly the same stage in regulated industries: the pilot impresses, the procurement review begins, and the deployment dies. The failure is not the model. It is the absence of governance, and it fails in five specific ways.
Reason one: answers that cannot be evidenced are answers that cannot be used
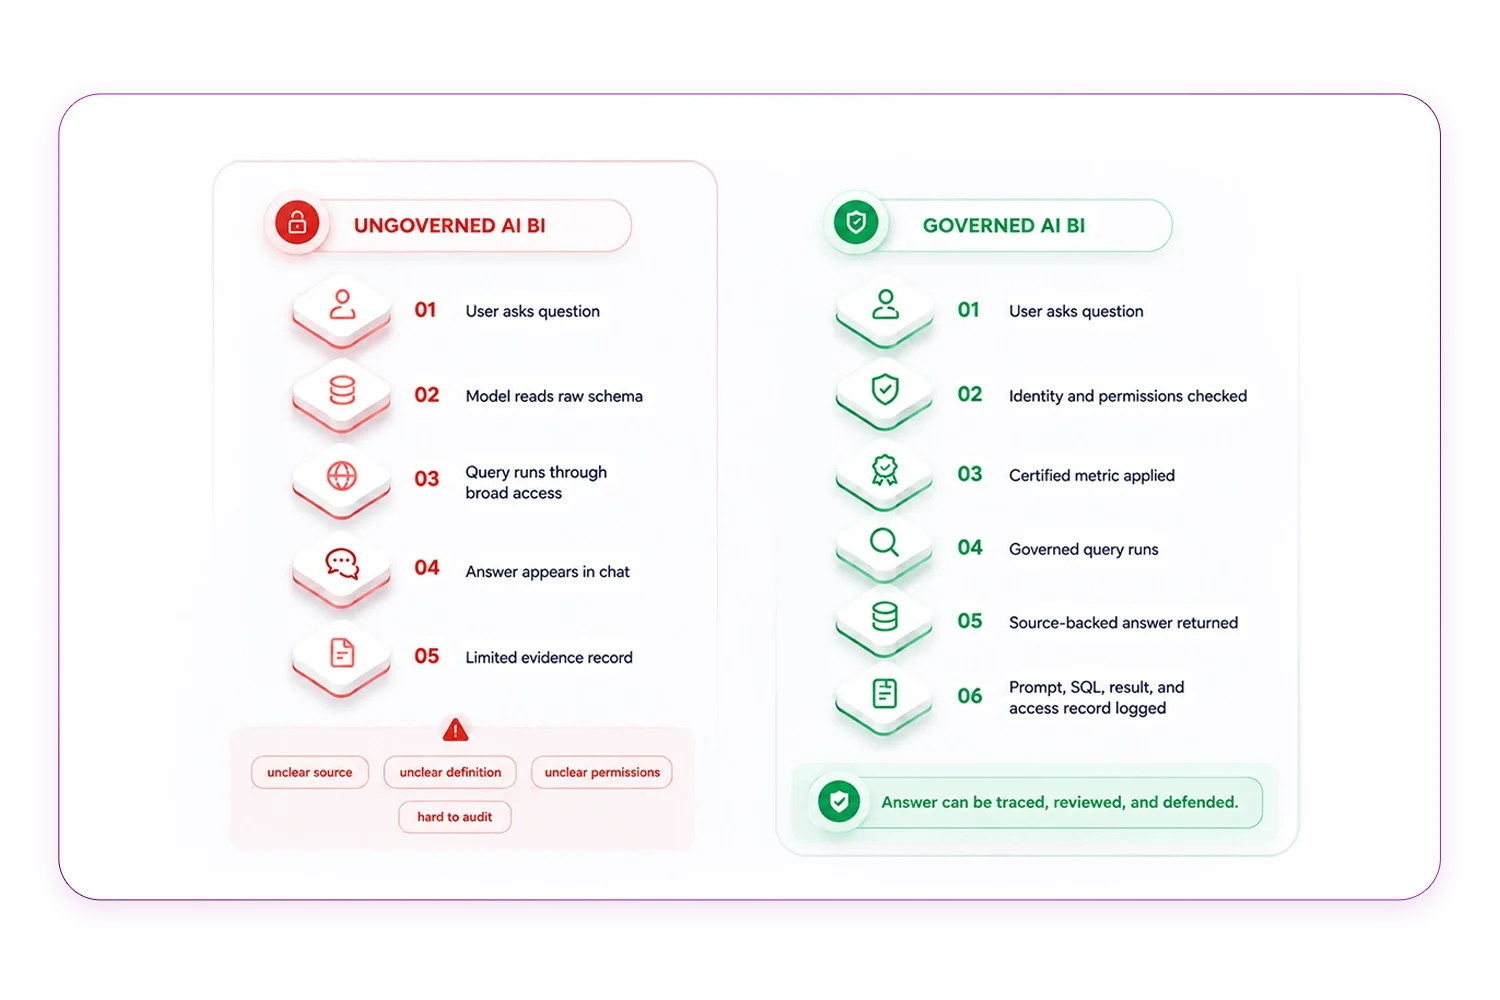
Regulated industries run on evidence. A number that reaches a regulator, an external auditor, or a filing must be supportable with documentation of its origin. An ungoverned AI BI tool produces answers in a chat window and retains, at best, a conversation history. There is no linked record of who asked, what SQL ran, which tables were read, or which definitions were applied. The tool’s answers may be perfectly correct, but correctness without evidence has no standing in a regulated process. The output is unusable for exactly the decisions that matter most, which confines the tool to trivia and guarantees it never justifies its cost.
Reason two: uncontrolled definitions produce contradictory numbers in official places
A model reading a raw schema must guess what the business means by its own vocabulary. Which of several revenue columns is the certified one? Are written premiums gross or net of reinsurance here? Does this health system count readmissions within 30 days or 90? An ungoverned tool answers these questions differently depending on phrasing, context, and chance. In an unregulated setting, that produces confusion. In a regulated one, it produces two different figures for the same metric in two official documents, and reconciling contradictory reported numbers is a process no compliance team enjoys. Without a certified semantic layer, this outcome is not a risk. It is a schedule.
Reason three: access control that lives outside the query path is access control in name only
Regulated data carries entitlement rules with legal force: patient records under health privacy law, material non-public information inside financial institutions, policyholder data under insurance regulation. Many AI BI tools connect to the warehouse through a single service account with broad read access, then rely on the application layer to decide what users should see. The moment the model generates an unanticipated query, that arrangement leaks. Governance means the agent inherits the asker’s permissions and enforces them at query time, so the question a user is not entitled to ask returns nothing, structurally, rather than being filtered by hope. Regulators examine the structural version. They penalise the other one.
Reason four: hallucinated analysis is fluent, and fluency defeats casual review
The dangerous failure mode of an ungoverned tool is not the visibly wrong answer. It is the plausible one: a well-formed figure, confidently presented, resting on a silently invented join or a misread column. Human review catches this only when the reviewer independently reproduces the work, which eliminates the time savings that justified the tool. Governed platforms attack this differently: grounding generation in certified definitions so there is less room to invent, and attaching the generated SQL and sources to every answer so verification takes minutes instead of hours. In a regulated industry, where an incorrect figure can constitute a reporting breach rather than an embarrassment, this difference is the whole game.
Reason five: the veto holders were never going to approve it
Enterprise AI deployments in regulated industries pass through three offices that each hold a veto: the CISO, the head of compliance, and increasingly the CFO. Each asks a governance question. The CISO asks how access is enforced and where data travels, including whether it leaves for a model vendor the organisation has not approved. Compliance asks how the system’s decisions will be documented for examiners. The CFO asks how a number can be traced when challenged. An ungoverned tool has no answer for any of the three, which means the deployment fails in procurement no matter how well the pilot went. The pattern repeats so reliably that it should be treated as a law of the category: in regulated industries, governance is not a feature of the deployment. It is the precondition for there being a deployment at all.
The conclusion regulated buyers are reaching
None of these five failures is cured by a better model, because none of them is a capability problem. They are control problems, and controls have to be architectural: a certified semantic layer, permissions enforced at query time, a complete prompt-level audit trail, and model choice the enterprise can direct. Platforms built this way clear the vetoes that kill their ungoverned rivals, and the results follow deployment rather than remaining in pilots. Based on QuaerisAI customer deployments and published materials, governed deployments have achieved BI adoption rates of 30 to 60 percent and reductions in BI cost of 70 percent, outcomes that are only available to tools that regulated enterprises are actually permitted to use.
Frequently asked questions
What counts as “AI BI without governance”?
Any deployment where a language model generates analysis against enterprise data without three controls in place: certified metric definitions the model must use, user-level access permissions enforced when the query executes, and a complete linked record of each interaction from prompt to SQL to result. A tool can be highly capable and still be ungoverned. The two properties are independent.
Are regulated industries simply late adopters of AI analytics?
No. They are early adopters of governed AI analytics and non-adopters of ungoverned AI analytics. The demand for faster answers is at least as strong in banking, insurance, and healthcare as anywhere else. What differs is that these industries cannot absorb the failure modes of ungoverned tools, so they wait for platforms where the controls are structural.
Can governance be added to an existing AI BI deployment later?
Partially, and expensively. Access enforcement and audit trails must live inside the query pipeline to be complete, which usually means the platform has to be built for them. Retrofitting typically produces fragmented logs and application-layer filtering, which are exactly the versions that fail examination. The practical answer is to evaluate for governance at selection, not remediation.